AI Security for SMBs: Data Breach Lessons

Adopting AI or external developers increases data-sharing risks, requiring updated internal controls. Based on late 2026 leaks, here are pre-AI checklists and records teams must maintain.
Contents
※Please be noted that this blog is translated automatically by AI
Summary
A data leak means unauthorized access to managed data.
AI adopters must check copied search docs and external tool inputs alongside existing systems.
SMBs are targeted too; size alone doesn't determine risk.
Check both login protection and user-specific access controls.
Define purpose, viewers, storage, and deletion for shared AI/vendor data.
Test AI where leads, approvals, and recovery are set; hold unverified data.


Member Data Leaks & Audit Focus
Registration and booking systems store IDs and contacts.
Below are company announcements as of Oct 15, 2026.
Times Car & Yakiniku King
Times Car detected unauthorized access on Sep 25.
Its 2nd report cited ~6.6M leaked accounts, including past users.
The 3rd report on Sep 29 noted ~1.6M IDs leaked.
These scopes differ and cannot simply be added.
Monogatari Corp announced 10,788,963 leaked Yakiniku King app records on Oct 5.
Breach detected Oct 2, confirmed Oct 3.
The entry vector was under review at release.
Lawson Incident & Review Checklist
Lawson reported leaks of 2,155,345 Lawson IDs and 26 app bookings on Oct 8.
The user-display system was compromised.
Attack methods cannot be assumed identical across the three.
Review your stored data types, post-cancellation retention, and display controls.
No AI involvement was confirmed in these reports.
SME Damage & Statistics Guide
Major data breaches are not just others' problems.
In H1 2026 NPA data, small/mid-sized firms (SMEs) accounted for ~60% of ransomware victims.
Ransomware encrypts data and demands ransom for restoration.
Victim Share vs. Actual Risk
The 60% figure is the share among reported victims.
It does not mean 60% of all SMEs were hit, nor does it show comparative risk by firm size.
However, it proves SMEs are indeed targeted.
In a 2024 IPA survey, 35.1% of 975 affected firms reported personal data leaks.
This is a multiple-choice rate among victims, not of all SMEs nationwide.
Prioritizing Data and Operations
Prioritize based on held data and downtime impact.
Resumes, client contacts, and billing data vary in access rights and recovery priority.
Executives and IT staff must first identify critical data and vital business operations.
Data Access Paths Growing with AI/RAG
GenAI input and internal AI search route data differently.
As of Oct 2026, check vendor terms and internal search designs separately.
Data input to external AI
The PPC urges checking if personal data inputs stay within stated purposes.
Also verify uses beyond output generation, like model training.
Approved AI may still restrict resumes or client lists.
Admins should check retention, deletion, and access scopes to define allowed data per task.
Removing names alone may not prevent re-identification via work history or affiliations.
Documents copied to internal AI search
RAG retrieves internal docs to inform AI answers.
Using a high-privilege service account to index data risks exposing restricted info company-wide.
Microsoft's doc-level access controls detail user matching and permission syncing.
Ensure changes or deletions in source files sync to chunked search data.
Test that restricted files, like HR interview notes, do not leak to unauthorized users.
After permission updates, verify past answers and cached data do not retain sensitive content.
Related articles

For RAG-based internal AI search, simply uploading documents to a vector DB is not enough. This article outlines key preparation areas—data, documents, permissions, update ownership, and search quality—from a practical perspective.
Web/App & Admin Check
Authentication verifies identity; authorization sets permissions.
Record both separately during checks.
Admin & Remote Access Authentication
List remote access (email, cloud, admin portals, VPN) and check admins.
A VPN connects remotely to internal networks.
MFA adds verification factors beyond passwords.
Prioritize admins and external accounts; disable unused ones.
Log enabled settings, targets, and exception reasons.
MFA cannot fix vulnerabilities, so check update status and EOS dates with maintainers.
For unsupported devices, set access limits and replacement plans.
Set log storage and reviewers to monitor suspicious logins regularly.
User Display & Access Scope
Have developers test different roles in staging.
Verify that others' data is blocked both on-screen and via backend APIs.
Hiding buttons does not ensure restricted access.
Document tested features, roles, and expected vs. actual results.
If unauthorized data appears, restrict the feature and halt release or AI integration until fixed.
External sharing & termination
When sharing data with contractors, define the purpose and person in charge.
Specify the scope needed and post-task data handling upfront, globally.
Task-Specific Access Rights
Take joint Japan-India development for inquiry features as an example.
Use mock data for UI testing instead of full production customer lists.
If real data is needed, an approver limits fields and duration to individual accounts.
Shared IDs hinder traceability.
Beyond NDAs, set clear rules on sub-contractors, local saves, and GenAI use.
When working across borders, assign decision-makers, local liaisons, and incident paths.
Consult legal on storage locations and contracts for cross-border personal data access.
Offboarding & Handover Logs
Admins revoke accounts and credentials once tasks end.
Clients must ensure contractors delete shared-folder files, local downloads, indexed copies, and chat attachments.
Log retention limits and usage bans for backups that cannot be wiped instantly.
For IDs and candidate data, separate deletable items from legally mandated archives.
Apply the same exit steps to personnel changes and archive the completion records.
Related articles
More companies want AI agents for support, sales docs, knowledge search, and project tracking. This article covers key points before outsourcing AI development: permissions, auth, approvals, audit logs, and acceptance criteria.
Backup & Incident Preparedness
Verify backups and actual recovery separately.
Review procedures and roles using IPA's SMB guidelines v4.0.
Restore Verification Scope
IT staff must restore data to an isolated test environment and verify usability.
Check file access, permissions, and business app integrations.
Review backup storage if production admin rights can modify or delete backups.
Log the affected operations, backup timestamp, recovery duration, and unrecovered data.
Align with management's acceptable downtime and data loss, adjusting frequency or storage as needed.
Remember that backups cannot retrieve leaked data.
Incident Contacts and Evidence Preservation
Predefine contacts (management, IT admin, vendor) and who can order disconnections.
If anomalies appear, prevent damage spread, preserve logs/evidence with experts, and log all actions.
Do not initialize or overwrite systems without authorization to avoid losing evidence.
For suspected personal data leaks, check PPC reporting/notification rules and deadlines.
Do not delay initial response while investigating causes; consult police and experts promptly.
SME Initial Check & AI Adoption
In the initial audit, management appoints a lead, and staff submit review records.
These items are Phinx's practical checks, not official standards.
Review Records Kept by Staff
Tool adoption alone does not prove controls work.
Pair owners with evidence to clarify unverified items.
Data Location: Staff log storage, use, viewers, and retention limits.
Authentication: Admins verify MFA scope, exceptions, and device updates.
Authorization: Devs record tests preventing unauthorized data access.
External Sharing: Buyers track recipients, AI input rules, and revoking access.
Recovery: IT logs gaps between test restores and management targets.
AI Connection: Deployers log purpose, approved data, terms, and role changes.
Limited Trials Excluding Unverified Scope
Connecting to AI requires data ownership, approval, and verified recovery.
If any item is unverified, hold the connection.
Meeting these does not guarantee safety; legal terms and pre-launch checks are still needed.
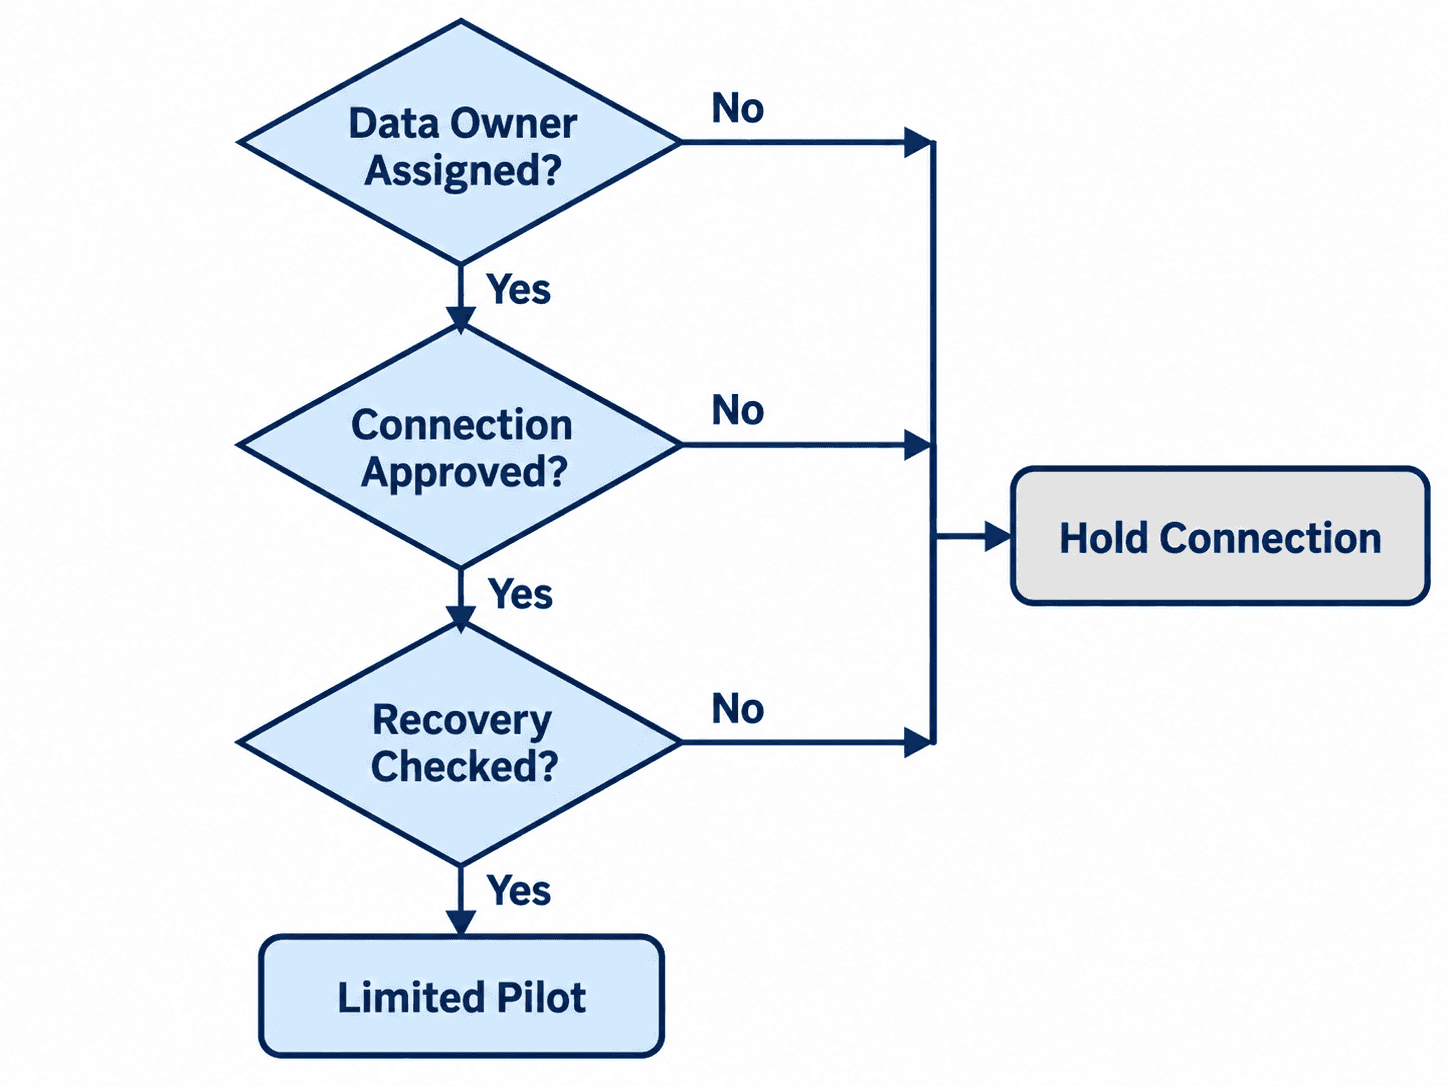
The chart evaluates ownership, access approval, then recovery.
Test with approved data and limited users, expanding only after confirming safety.
Testing without live customer data can run alongside remediation.
Summary
SME data breach prevention requires aligning stored data with business operations.
Member records, IDs, and applicant data carry different risks and access needs.
Sharing rules must maintain these distinctions when adopting AI or external talent.
For the initial review, leaders must assign managers to log all findings.
Verify auth checks, contractor offboarding, and data recovery per workflow.
For AI data, review scope, permissions, and terms, starting only with approved sets.
Validating app access, cloud rights, and search indexing burdens non-dedicated staff.
When outsourcing, clients define access while vendors document test results.
Written records ensure seamless, repeatable audits even after staff changes.
Revisit review logs when integrating new tools or switching vendors.
Defining clear scopes lets teams use AI safely without seeking repeated approvals.
Phinx builds data foundations with global dev teams, managing end-to-end operations.
We design unified data usage and administrative roles tailored to company scale.
Sources
Times Car: "Unauthorized Access Investigation & Countermeasures (Report 2)" (Published Sep 28, 2026; Updated Oct 1)
Times Car: "Unauthorized Access Investigation & Countermeasures (Report 3)" (Published Sep 29, 2026; Updated Oct 1)
Monogatari Corp: "Apology for Data Breach via Unauthorized App Access" (Oct 5, 2026)
Lawson: "Apology and Notice on Data Breach via Unauthorized Access" (Oct 8, 2026)
NPA: "Cyberspace Threat Landscape for H1 2026" (pp. 10–11)
IPA: "FY2024 SME Survey Preliminary Results" (Feb 14, 2025)
IPA: "FY2024 SME Information Security Survey Report" (May 27, 2025)
PPC: "Guidance on Using Generative AI Services" (Jun 2, 2023, Att. 1)
Microsoft: "Document-level access control in Azure AI Search"
IPA: "SME Information Security Guidelines v4.0"
PPC: "Data Breach Response Resources"
Latest Articles
Stay up-to-date
Related articles

India University Tiers & Hiring: Salary Data & Candidate Assessment

AI Subsidies: What to Outsource vs. In-house or SaaS
AI Security for SMBs: Data Breach Lessons

Stricter Visa Rules for Dispatched Engineers in Japan (2026)